Keystone Website Breach Exposes Crypto Wallet Buyers’ Addresses and Purchase Details
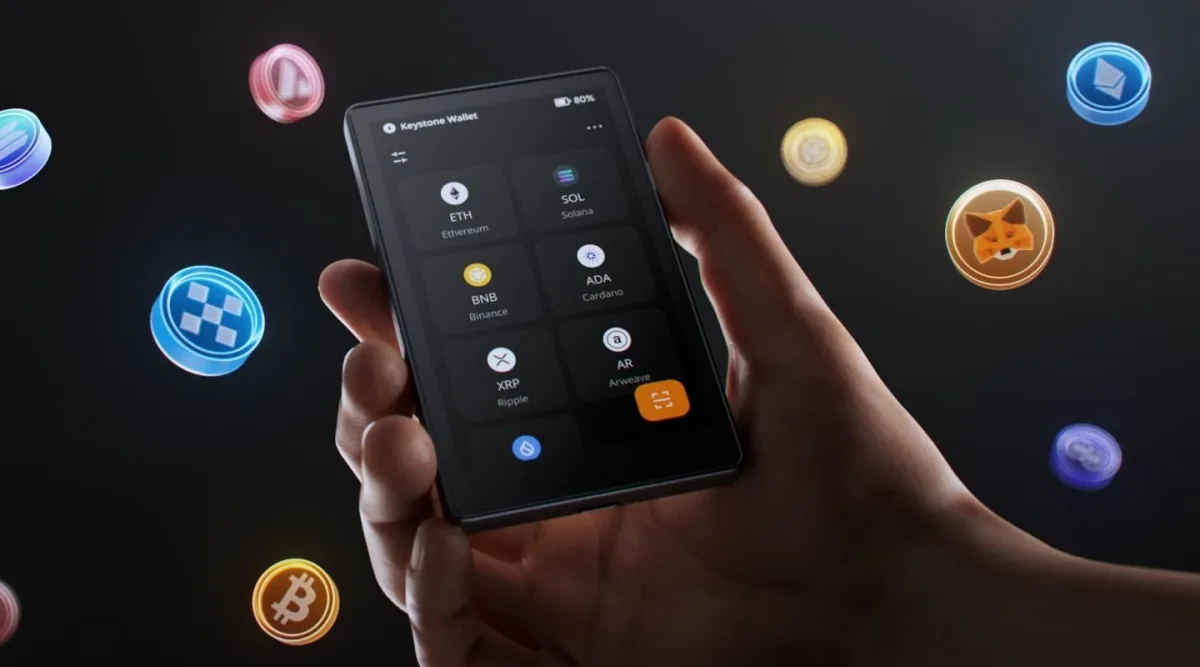
Crypto hardware wallet maker Keystone disclosed a security breach on October 24, 2026, exposing customers’ personal information and shipping addresses. The company detected unauthorized website access on October 20 and confirmed the data theft on October 23 after reviewing Shopify API activity. Compromised records included customer names, contact details, delivery addresses, purchased products, and prices. Keystone has not disclosed how many customers were affected.
The company said payment information, recovery phrases, private keys, and wallet passwords remained secure. However, security researcher Taylor Monahan warned that exposed addresses could enable targeted phishing, robbery, and kidnapping attempts. Blockchain security firm CertiK recorded 52 verified physical attacks against cryptocurrency holders during the first half of 2026, a 33% increase from the previous year.
Meanwhile, the incident raised questions about Keystone’s customer data retention practices. The company previously promised to delete shipping information after 180 days. However, some customers reported receiving breach notifications despite purchasing wallets more than two years earlier. Keystone said it blocked unauthorized access, fixed the vulnerability, and began notifying affected customers. It also launched an investigation and promised a detailed report.
Why it matters
The breach highlights security risks beyond cryptocurrency theft. Exposed personal information could make hardware wallet owners vulnerable to sophisticated scams and physical attacks.